FreeIPA Flaw Chain Lets Anonymous Clients Create Reusable Administrator Credentials
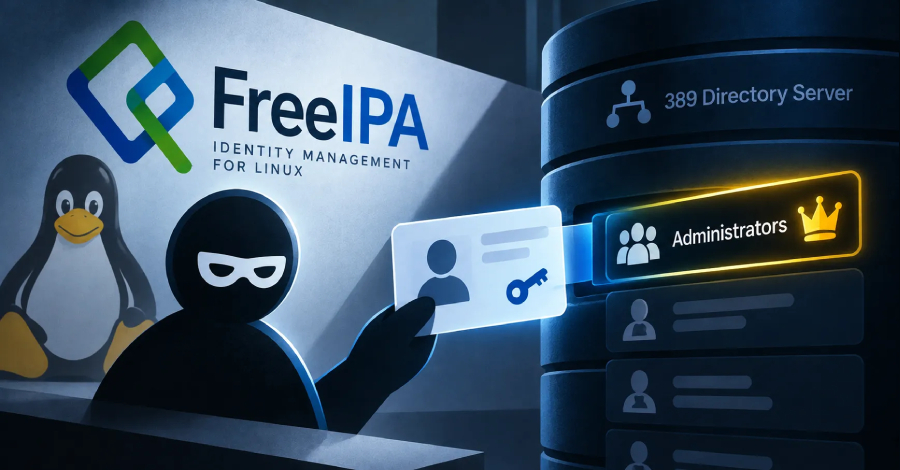
A flaw in FreeIPA lets a client that has never logged in create a Kerberos identity of its own choosing in the directory and end up in the administrators group, Red Hat says. FreeIPA is the system that determines who may log in across a Linux domain and maintains all identities in a 389 Directory Server database accessed via LDAP. The attack needs a second flaw in that database software. The
لماذا يهم هذا الخبر؟
سيظهر الملخص التحليلي هنا بعد اكتمال معالجة الذكاء الاصطناعي.
سياق الخبر
A flaw in FreeIPA lets a client that has never logged in create a Kerberos identity of its own choosing in the directory and end up in the administrators group, Red Hat says. FreeIPA is the system that determines who may log in across a Linux domain and maintains all identities in a 389 Directory Server database accessed via LDAP. The attack needs a second flaw in that database software. The
فتح الخبر الأصلي