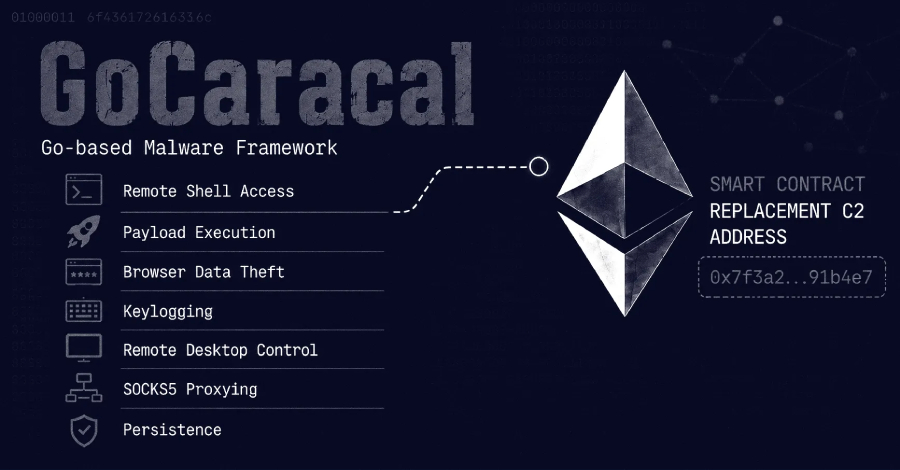
GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address
Threat actors linked by Arctic Wolf to Dark Caracal with medium confidence deployed a previously undocumented Go-based malware framework, GoCaracal, during a June 2026 intrusion at an unnamed communications organization in Venezuela. GoCaracal provides operators with remote shell access and payload execution, while the extended profile adds browser data theft, keylogging, remote desktop control
لماذا يهم هذا الخبر؟
سيظهر الملخص التحليلي هنا بعد اكتمال معالجة الذكاء الاصطناعي.
سياق الخبر
Threat actors linked by Arctic Wolf to Dark Caracal with medium confidence deployed a previously undocumented Go-based malware framework, GoCaracal, during a June 2026 intrusion at an unnamed communications organization in Venezuela. GoCaracal provides operators with remote shell access and payload execution, while the extended profile adds browser data theft, keylogging, remote desktop control
فتح الخبر الأصلي