Marimo Notebook Flaw Could Run MCP Commands Before Cells Execute in Edit Mode
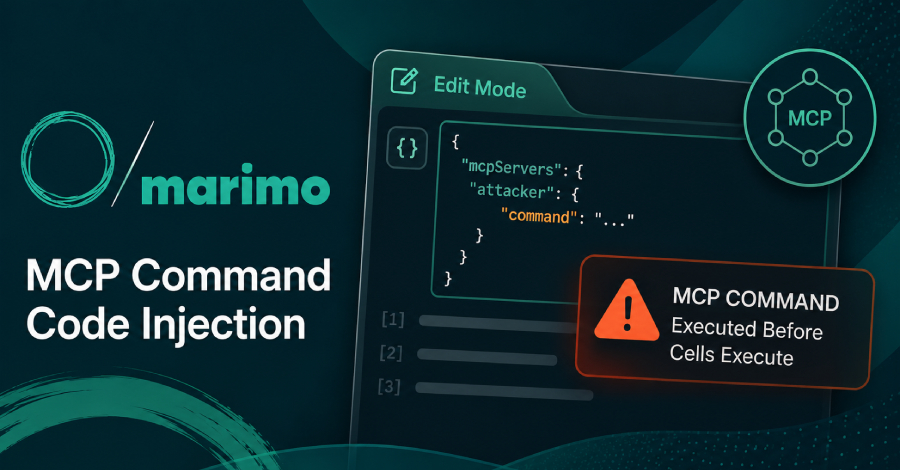
Marimo has addressed a high-severity security flaw in its notebook software that allowed an attacker to execute an attacker-supplied Model Context Protocol (MCP) command in a specially crafted notebook, according to VulnCheck's CVE Numbering Authority (CNA) record. The CNA record says the command can run as a local subprocess when the notebook is opened in edit mode. The vulnerability, tracked
لماذا يهم هذا الخبر؟
سيظهر الملخص التحليلي هنا بعد اكتمال معالجة الذكاء الاصطناعي.
سياق الخبر
Marimo has addressed a high-severity security flaw in its notebook software that allowed an attacker to execute an attacker-supplied Model Context Protocol (MCP) command in a specially crafted notebook, according to VulnCheck's CVE Numbering Authority (CNA) record. The CNA record says the command can run as a local subprocess when the notebook is opened in edit mode. The vulnerability, tracked
فتح الخبر الأصلي