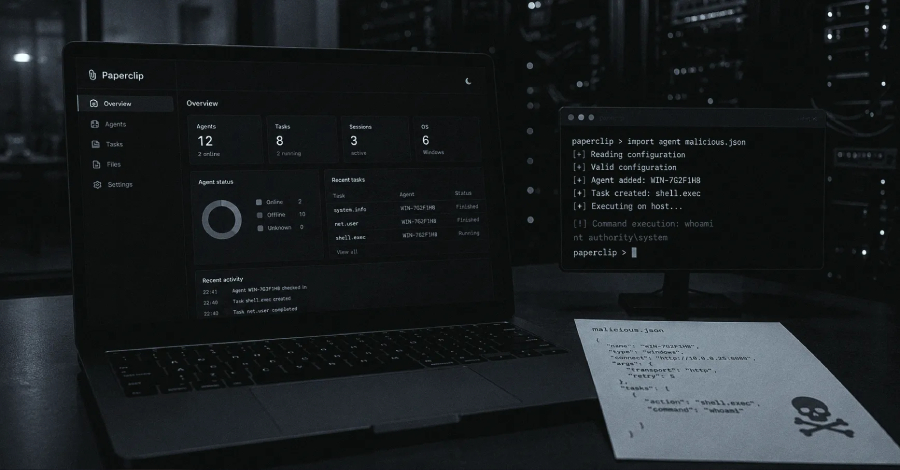
Paperclip AI Flaws Let Attackers Run Host Commands via Malicious Agent Imports
Two security flaws in Paperclip could let attackers execute commands on a network server or a developer's computer. Paperclip is an open-source control plane for teams of artificial intelligence (AI) agents, and both paths rely on importing a malicious agent and starting it. A third flaw could expose sensitive data and control-plane details through application programming interface (API) routes
لماذا يهم هذا الخبر؟
سيظهر الملخص التحليلي هنا بعد اكتمال معالجة الذكاء الاصطناعي.
سياق الخبر
Two security flaws in Paperclip could let attackers execute commands on a network server or a developer's computer. Paperclip is an open-source control plane for teams of artificial intelligence (AI) agents, and both paths rely on importing a malicious agent and starting it. A third flaw could expose sensitive data and control-plane details through application programming interface (API) routes
فتح الخبر الأصلي