ثغرة Gitea تسمح بتنفيذ أوامر خطيرة
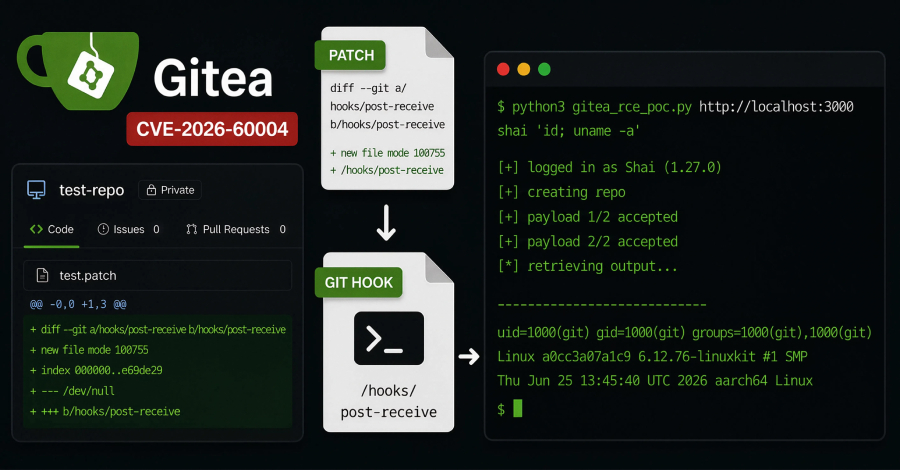
تم إصلاح ثغرة أمنية حرجة في منصة Gitea ذات الاستضافة الذاتية، تسمح للمهاجمين بتنفيذ أوامر عبر Git hook. تؤثر الثغرة على الإصدارات 1.17 وما بعدها قبل 1.27.1 وتم إصلاحها في 1.27.1.
لماذا يهم هذا الخبر؟
تسلط هذه الثغرة الضوء على أهمية تحديث البرمجيات بشكل دوري، خاصةً تلك المستخدمة في بيئات الاستضافة الذاتية، لحماية الأنظمة من الهجمات المحتملة.
سياق الخبر
Gitea, the self-hosted Git platform, has patched a critical remote code execution vulnerability. A user with ordinary repository write access can turn attacker-controlled patch content into a live Git hook and run shell commands as the Gitea service account. Tracked as CVE-2026-60004 (CVSS score: 9.8), the flaw affects Gitea versions 1.17 and later before 1.27.1 and is fixed in 1.27.1. The
فتح الخبر الأصلي