استكشاف ضعف في Linux Traffic-Control Exploit
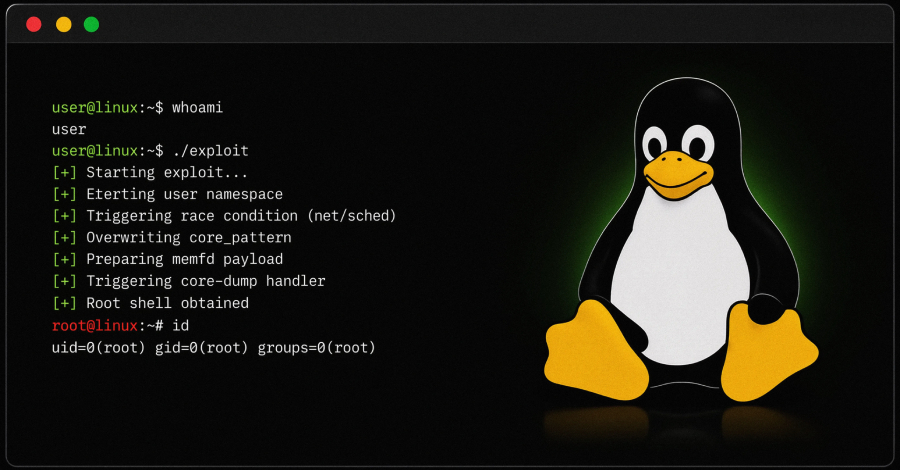
استكشاف ضعف في نظام حماية الشبكة لLinux مع استهداف CentOS Stream 9
لماذا يهم هذا الخبر؟
هذا الاختراق يشير إلى وجود عيوب في在网络交通控制方面 ل hệ التشغيل Linux. استهداف CentOS Stream 9 يظهر أن هذا الخطأ يمكن الوصول إليه عبر بنية النظام.
سياق الخبر
STAR Labs has published a Linux kernel exploit that turns an ordinary local user into root on the CentOS Stream 9 build it targeted. The flaw, tracked as CVE-2026-53264 (CVSS score: 7.8), is a use-after-free race in the kernel's network traffic-control subsystem.Researcher Lee Jia Jie said artificial intelligence (AI) helped him find the bug and speed up exploit development. This is local
فتح الخبر الأصلي